Field Notes
Write-ups on network architecture, infrastructure, and security.
Tagged #grc× Clear tag
Threat & DefenseAdvanced· 4 min
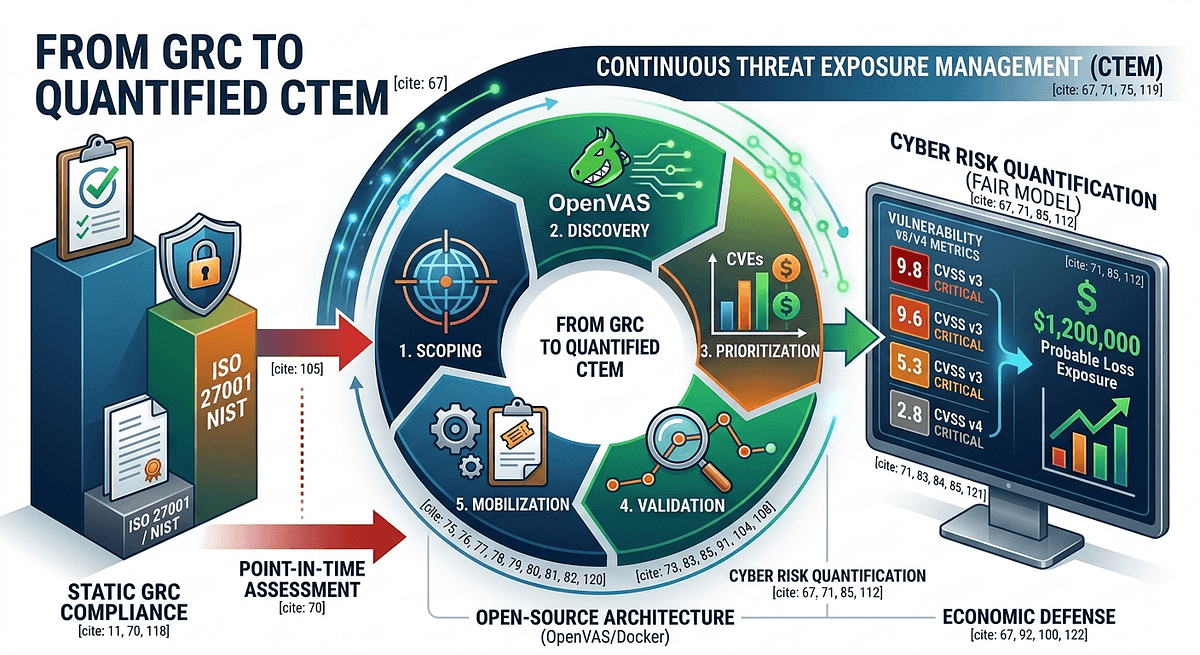
From GRC Compliance to Continuous Exposure Management: Quantifying Cyber Risk with Open-Source Architecture
Introducing a Continuous Threat Exposure Management (CTEM) framework integrated with FAIR cyber risk quantification: moving from static GRC compliance to continuous, board-level risk visibility.
Sep 14, 2026
Threat & DefenseAdvanced· 4 min
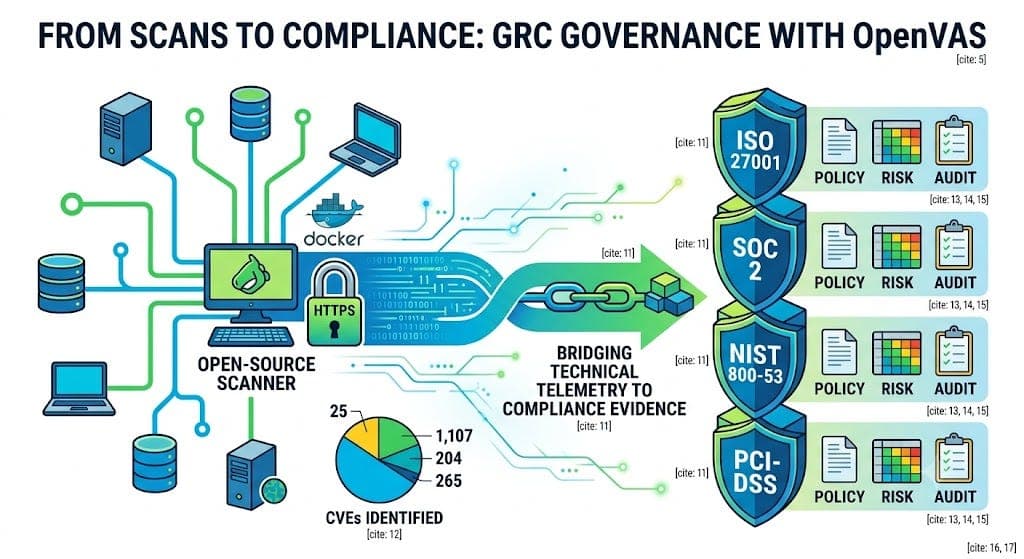
Bridging Technical Scanning to Enterprise Governance: How Open-Source Vulnerability Management Drives GRC Compliance
How open-source vulnerability scanning workflows transform raw system telemetry into auditable compliance evidence across ISO 27001, SOC 2, NIST SP 800-53, and PCI-DSS.
Sep 14, 2026
Get new posts by email: no spam, unsubscribe anytime.