Field Notes
Write-ups on network architecture, infrastructure, and security.
Compounding Discipline: How It All Reinforces Itself
Why security, process, and planning don't work as well in isolation as they do together
Sep 25, 2026
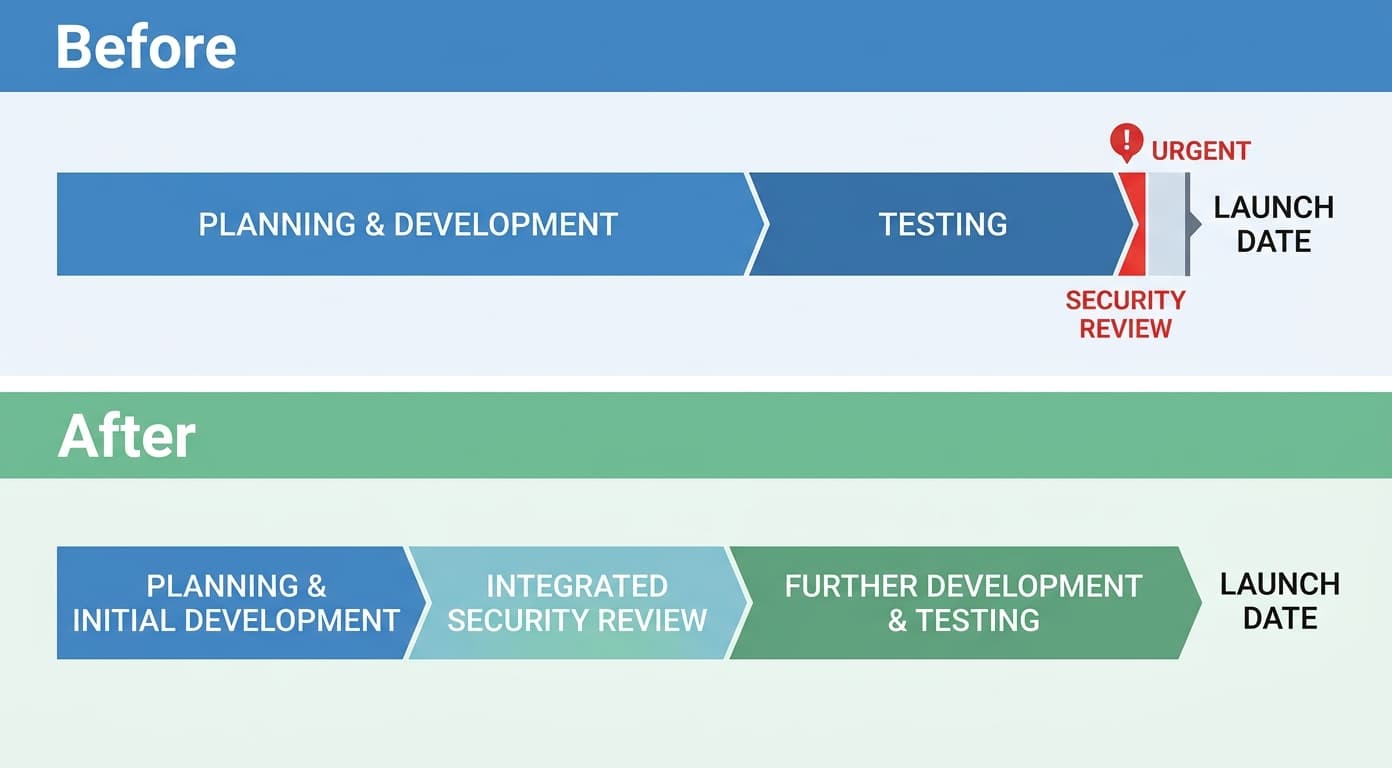
The Overlooked Power of Project Management in Engineering
Why the discipline that keeps a project organized is, quietly, also a security and quality discipline
Sep 25, 2026
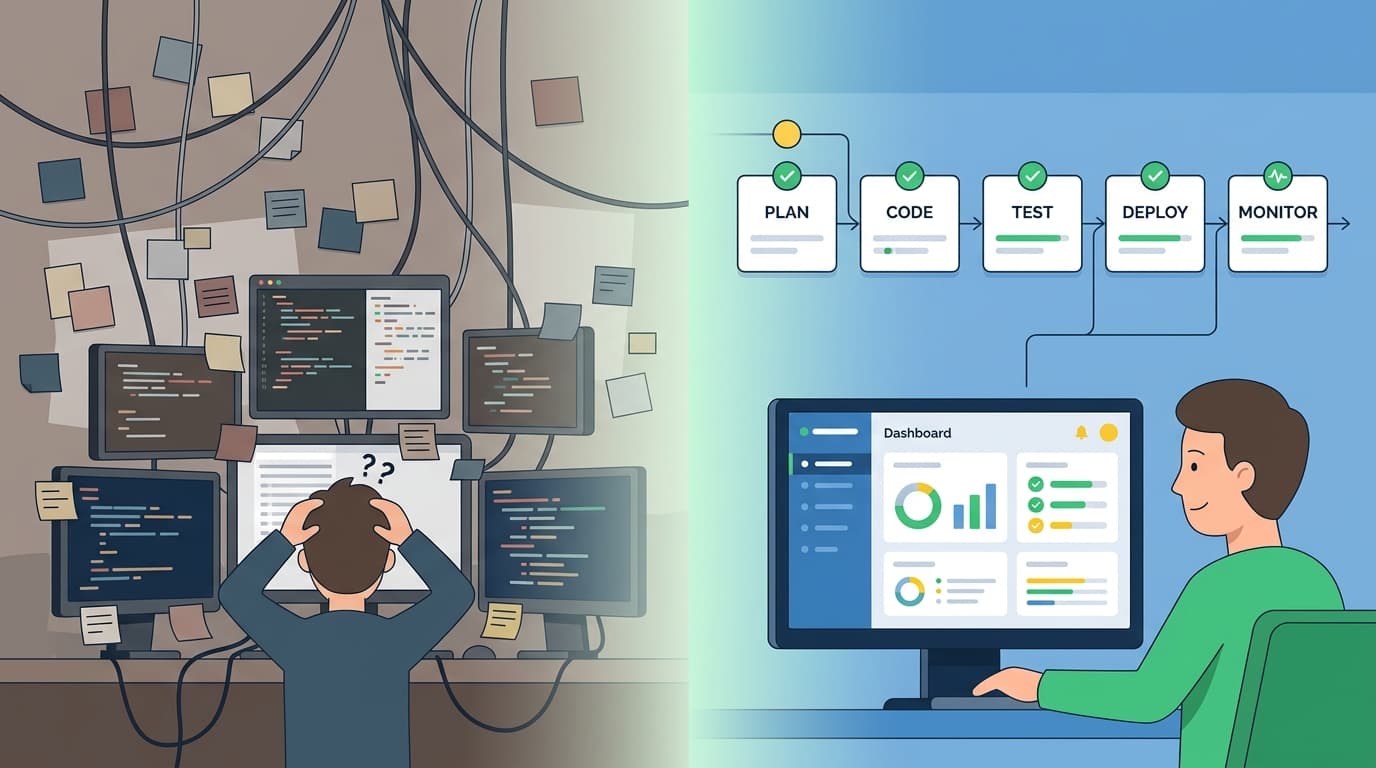
Why Process Beats Heroics in Software Development
An organized development process isn't bureaucracy; it's what keeps quality and security from depending on any one person's memory
Sep 25, 2026
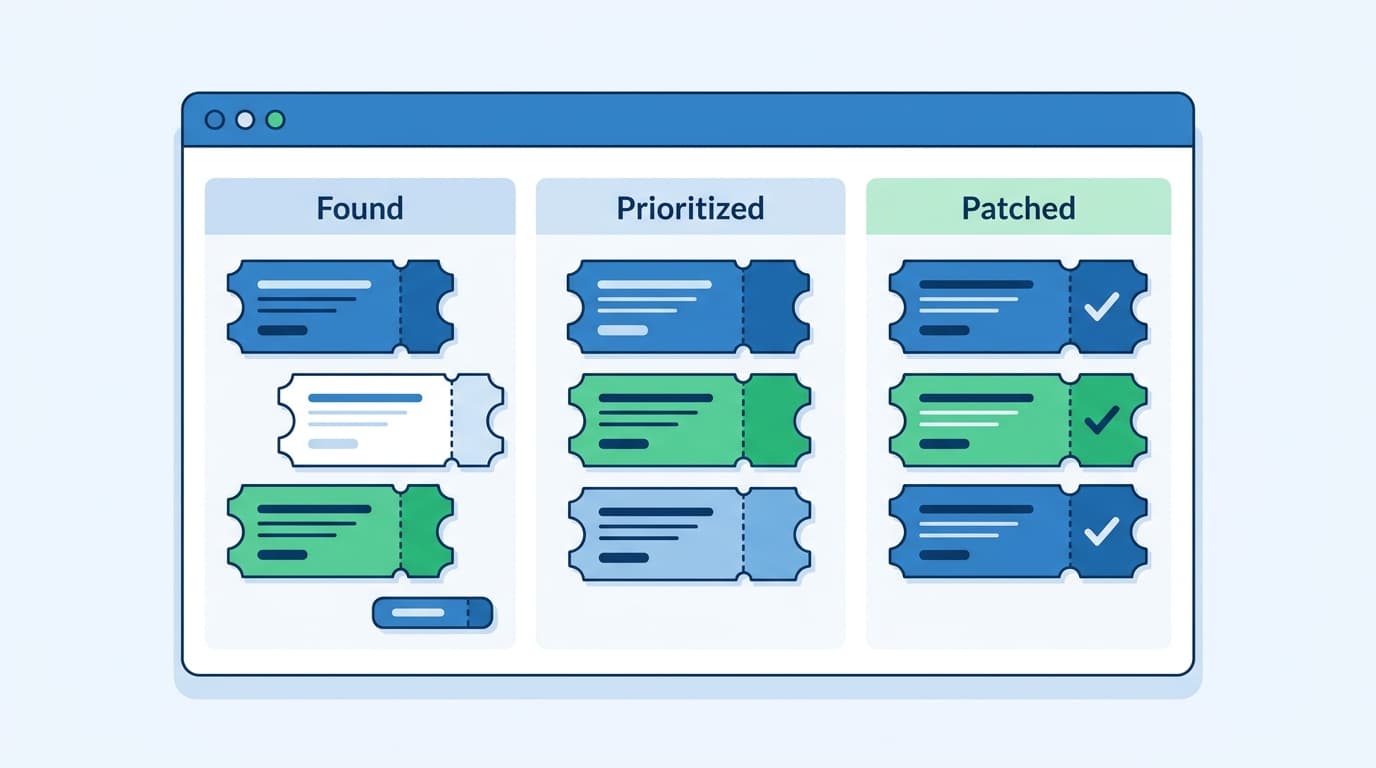
Vulnerability Management: Find It, Prioritize It, Patch It
A practical look at the unglamorous discipline that decides whether known flaws get fixed before or after they're exploited
Sep 25, 2026
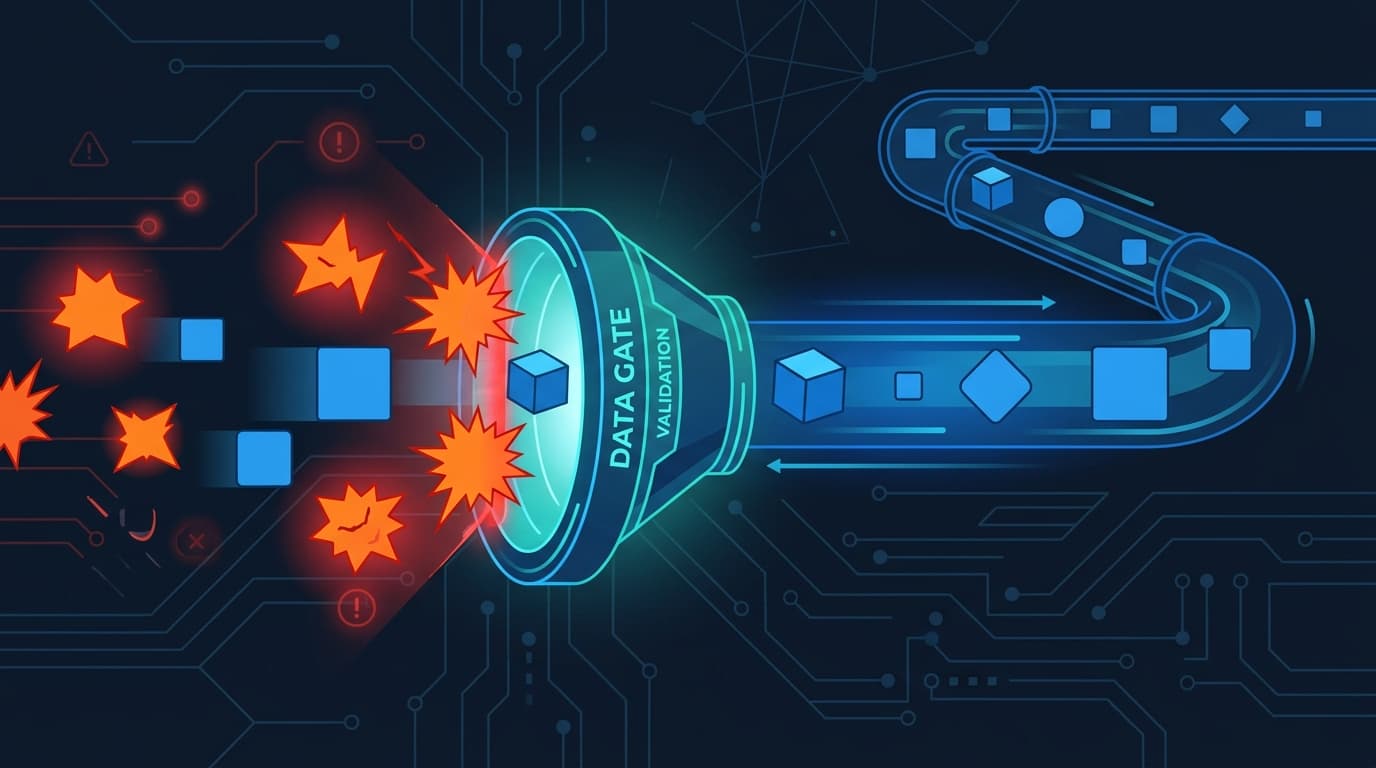
The Discipline of Input Validation
Why trusting input is how systems break, and why validation is the cheapest security control you'll ever implement
Sep 25, 2026
Why Cybersecurity Actually Matters
Beyond the headlines: what's really at stake, and why it's everyone's job, not just the security team's
Sep 25, 2026
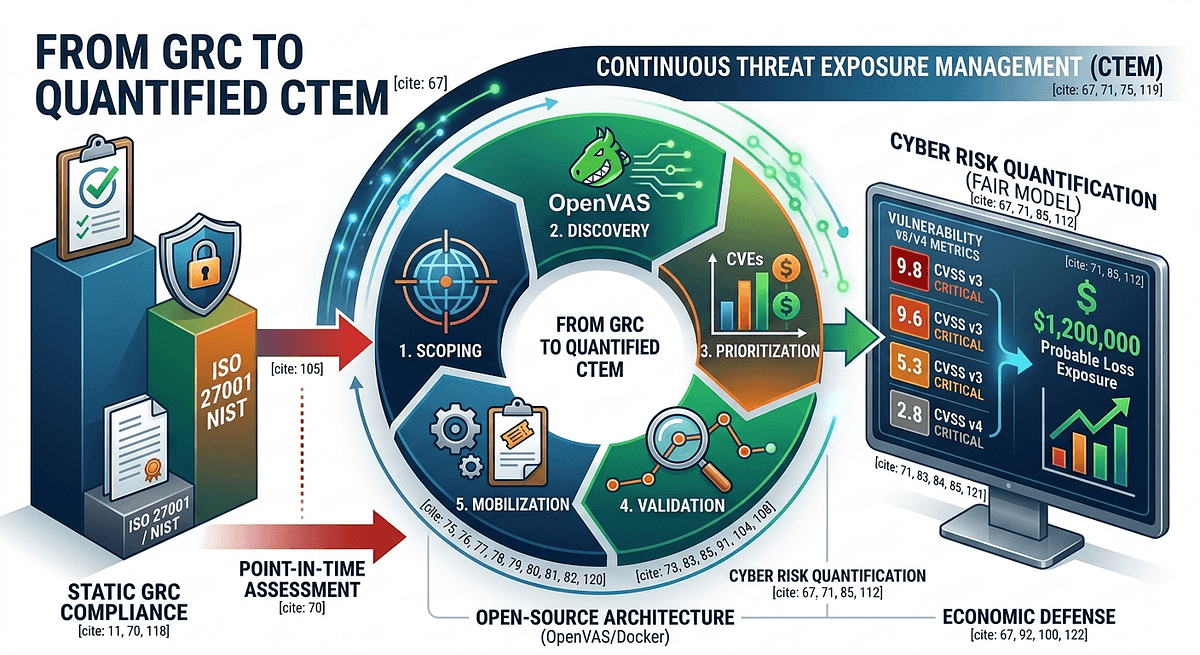
From GRC Compliance to Continuous Exposure Management: Quantifying Cyber Risk with Open-Source Architecture
Introducing a Continuous Threat Exposure Management (CTEM) framework integrated with FAIR cyber risk quantification: moving from static GRC compliance to continuous, board-level risk visibility.
Sep 14, 2026
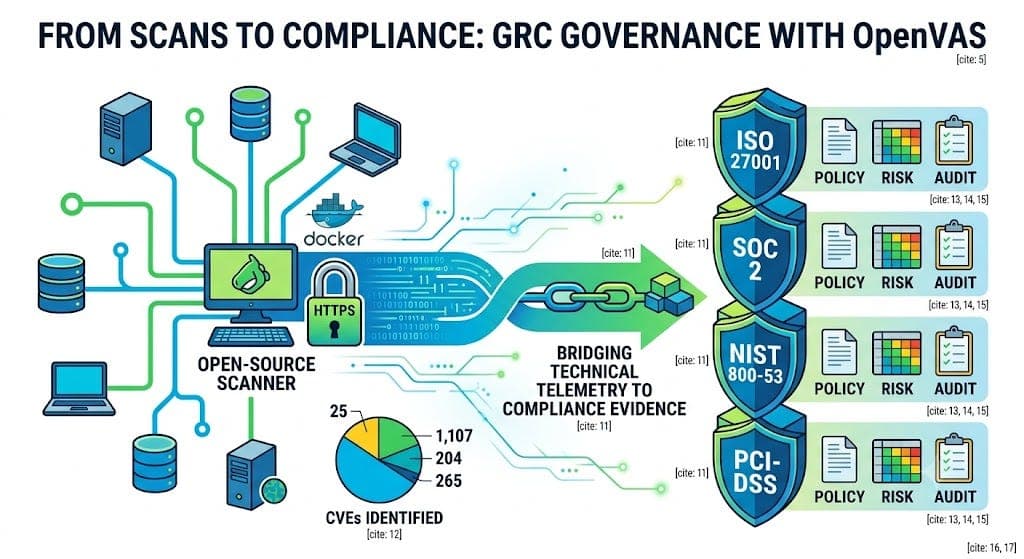
Bridging Technical Scanning to Enterprise Governance: How Open-Source Vulnerability Management Drives GRC Compliance
How open-source vulnerability scanning workflows transform raw system telemetry into auditable compliance evidence across ISO 27001, SOC 2, NIST SP 800-53, and PCI-DSS.
Sep 14, 2026
Get new posts by email: no spam, unsubscribe anytime.