Field Notes
Write-ups on network architecture, infrastructure, and security.
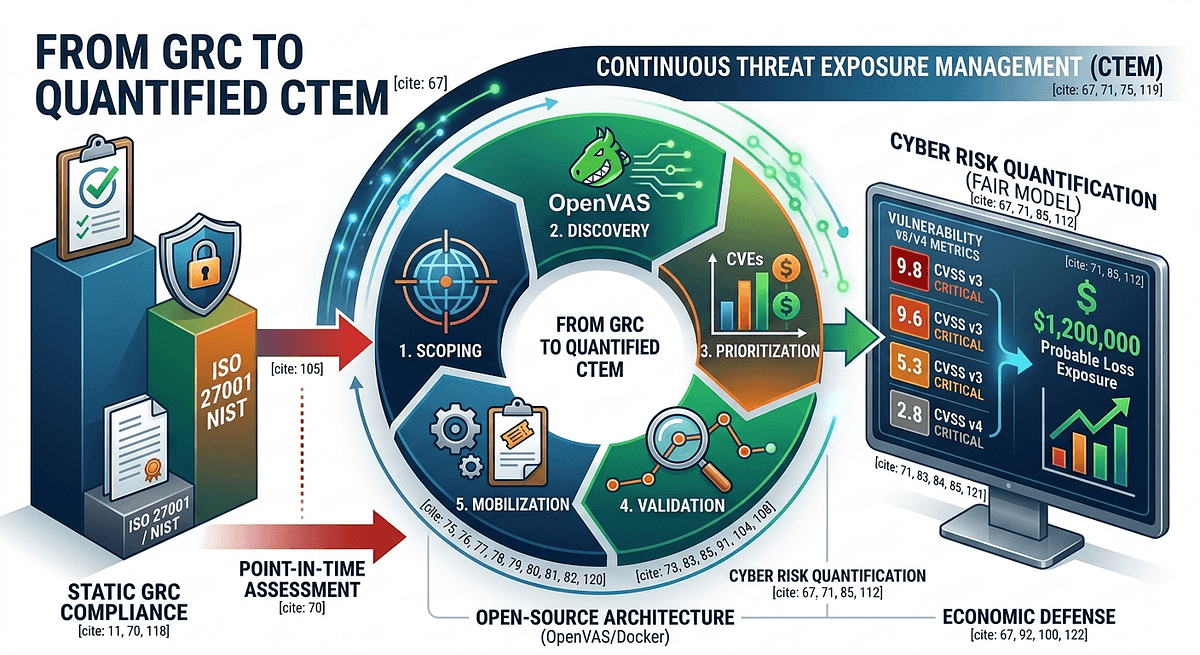
From GRC Compliance to Continuous Exposure Management: Quantifying Cyber Risk with Open-Source Architecture
Introducing a Continuous Threat Exposure Management (CTEM) framework integrated with FAIR cyber risk quantification: moving from static GRC compliance to continuous, board-level risk visibility.
Sep 14, 2026
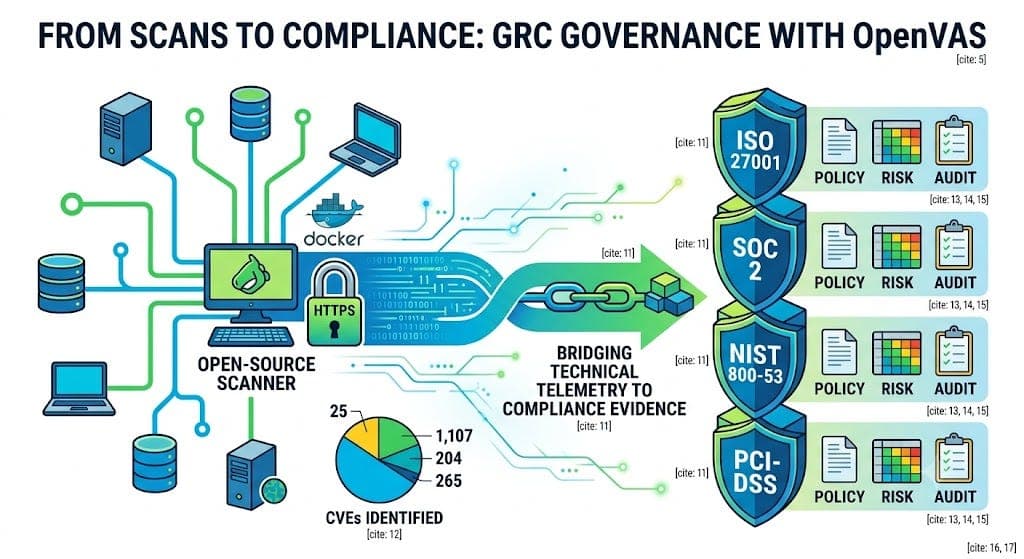
Bridging Technical Scanning to Enterprise Governance: How Open-Source Vulnerability Management Drives GRC Compliance
How open-source vulnerability scanning workflows transform raw system telemetry into auditable compliance evidence across ISO 27001, SOC 2, NIST SP 800-53, and PCI-DSS.
Sep 14, 2026
Running OpenVAS Is Easy. Managing Vulnerabilities Is Not.
Vulnerability scanning is widely adopted, yet many organizations struggle to reduce risk despite running regular scans. Without governance, prioritization, and ownership, vulnerability data becomes noise.
Sep 14, 2026
OpenVAS Vulnerability Scanner on Ubuntu 24.04: Docker Deployment with HTTPS
How to run OpenVAS (GVM) in Docker with HTTPS on Ubuntu 24.04: consolidating the working steps where Greenbone's own documentation is partially outdated.
Sep 14, 2026
Get new posts by email: no spam, unsubscribe anytime.